Free Htaccess Ip Blocker Code Generator For Apache
Generate Apache .htaccess IP-blocking rules from addresses you specify. Review the generated directives for your server version before applying access restrictions.
Loading tool… if this message stays, JavaScript is blocked or failed to load — check your connection and console, then reload.
Free Htaccess Ip Blocker Code Generator
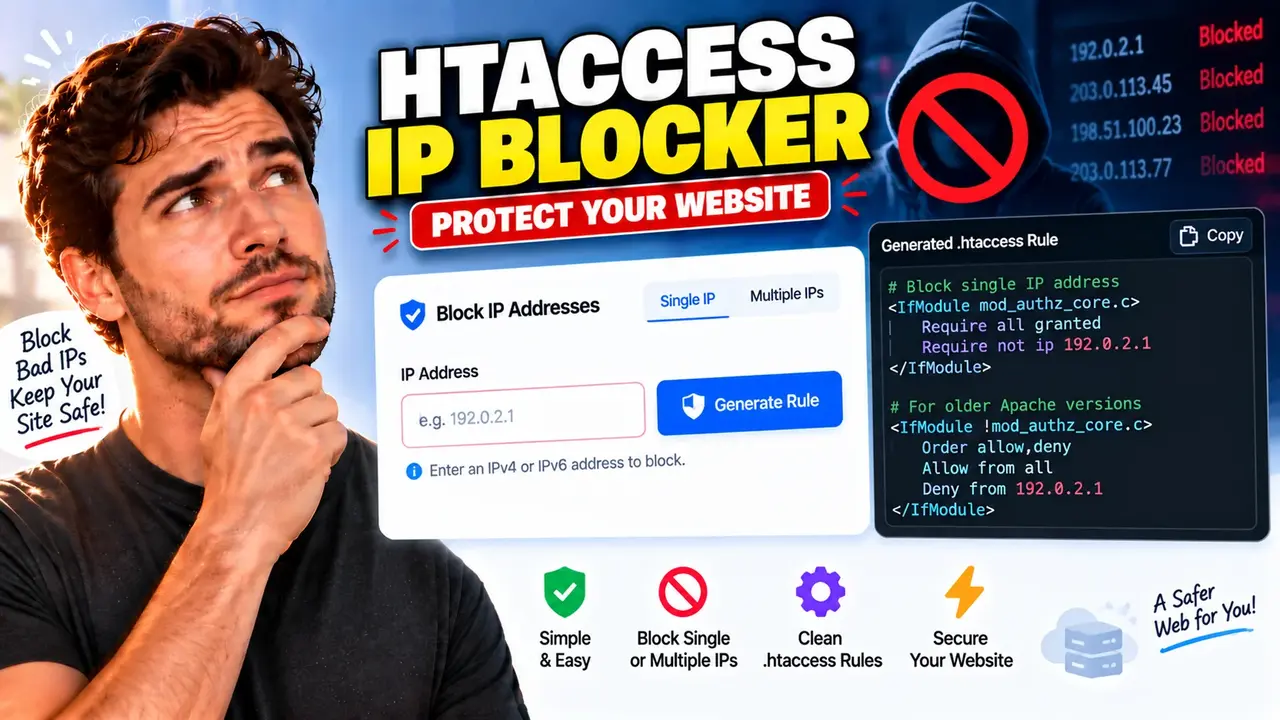
Quick answer: The Free Htaccess Ip Blocker Code Generator is a developer utility for preparing Apache .htaccess rules that deny access to specified IP addresses. It is intended to help website administrators create access-control directives for blocking unwanted IP traffic by generating configuration code from IP addresses supplied by the user.
Use the generated configuration as a starting point for restricting access to a website or directory hosted on an Apache server. Before deploying the rules, verify that the generated syntax matches your server version, existing access-control configuration, and intended blocking policy.
Key Takeaways
- Primary function: Generate .htaccess access-denial rules for IP-based restrictions.
- Input: The IP addresses to block.
- Output: Apache configuration directives intended for a .htaccess file.
- Best suited for: Website owners, web developers, and server administrators managing unwanted access.
- Important limitation: The generated rules must be checked against the Apache version and configuration in use.
How to Use Free Htaccess Ip Blocker Code Generator?
- Identify the IP addresses. Collect the IPv4 or IPv6 addresses you intend to restrict. Confirm that each address belongs to traffic you actually want to block.
- Enter the addresses. Supply the addresses using the input format supported by the generator. The exact separators, address validation, and supported address families should be confirmed in the live tool.
- Generate the configuration. Run the generator to obtain the corresponding .htaccess code.
- Review and deploy. Inspect the generated directives, back up your existing .htaccess file, and test the rules in a controlled environment before applying them to a production website.
Input and Output Example
The following example illustrates an Apache 2.4-style access restriction for a single IPv4 address. It is an illustrative configuration example, not a verified output captured from the live generator.
Input
203.0.113.25Illustrative output for Apache 2.4
<RequireAll>
    Require all granted
    Require not ip 203.0.113.25
</RequireAll>
The address 203.0.113.25 belongs to a documentation-only IPv4 range and is used here as an example. Replace it with the actual address you intend to restrict. The example uses Apache 2.4 authorization directives and must be tested in the context of the target directory and existing access rules.
IP Blocking Reference Table
| Input scenario | Illustrative directive | Purpose and caution |
|---|---|---|
| Block one IPv4 address | Require not ip 203.0.113.25 |
Denies authorization to the specified address when combined with the appropriate authorization container. |
| Block another IPv4 address | Require not ip 198.51.100.42 |
Illustrates a second address that can be included in a blocking policy. |
| Block an IPv4 subnet | Require not ip 198.51.100.0/24 |
Restricts an IPv4 network range rather than one host. Confirm that the entire range should be blocked. |
| Block an IPv6 address | Require not ip 2001:db8::25 |
Illustrates IPv6 syntax. Confirm IPv6 support and the generator's handling of address validation. |
| Permit everyone except selected addresses | Require all granted with appropriate negative IP requirements |
Requires correct authorization-container logic. Combining Apache authorization directives incorrectly can change the effective access policy. |
Important: The IP addresses in the examples use documentation ranges. They are not recommendations to block real users. These examples explain Apache syntax and are not evidence that the generator accepts CIDR ranges, IPv6, or multiple input formats.
How the IP Blocking Rules Work
A .htaccess file is a per-directory Apache configuration file. Where the server permits overrides, Apache reads applicable directives to determine how requests should be handled. IP-based authorization rules evaluate the client address visible to the web server and can deny access when the request matches a configured restriction.
For Apache 2.4, the authorization system includes directives such as Require all granted, Require not ip, and authorization containers such as <RequireAll>. A negative requirement generally needs to be combined with a positive authorization requirement to form a valid access policy. The precise behavior depends on the directive context and the complete configuration.
Older Apache configurations may use the legacy Order, Allow, and Deny directives. These belong to a different authorization syntax. Do not mix legacy and Apache 2.4 authorization styles without understanding the compatibility module and migration requirements.
Technical Edge Cases and Limitations
Apache version compatibility
Authorization syntax differs between Apache 2.2-era configurations and Apache 2.4. A generated rule that uses modern Require directives may not work in an older environment. Check the version and enabled modules before deploying generated code.
IP address versus proxy address
When a website is behind a reverse proxy, load balancer, or content delivery network, Apache may see the proxy's address instead of the original visitor's address. Blocking the wrong address can affect many legitimate users. Forwarded-IP headers should only be trusted when the server is configured to accept them from trusted proxies.
IPv4, IPv6, and CIDR ranges
IPv4 addresses, IPv6 addresses, and network ranges have different representations. Do not assume that the generator supports every address family or CIDR notation unless the interface confirms it. Validate each input and review the resulting directives.
Existing .htaccess directives
Access-control directives can interact with existing authorization containers, rewrites, application routing, and hosting-provider settings. Replacing an entire .htaccess file with a generated snippet may remove important rules. Integrate only the necessary directives and preserve a backup.
Invalid or empty input
Malformed addresses, empty entries, accidental whitespace, and incorrectly formatted network ranges can produce unusable or unintended configuration. The live generator's exact validation and error-handling behavior has not been established here. Inspect the generated output rather than assuming that all inputs have been validated.
Supported Use Cases and Limitations
Suitable use cases
- Preparing a deny rule for a known unwanted IPv4 address.
- Drafting access restrictions for a selected network range when the syntax is supported and verified.
- Creating a starting point for a website administrator to review and integrate into an existing .htaccess file.
Limitations to consider
- The generator's exact input separators and address-validation rules are not established by the supplied information.
- Support for IPv6, CIDR ranges, bulk lists, and Apache versions must be confirmed in the actual interface.
- A generated rule does not establish that the hosting provider allows the required .htaccess overrides.
- IP blocking is not a complete security solution and does not replace application authentication, rate limiting, firewall policies, or server-level access controls.
Security and Deployment Guidance
Use IP restrictions as one layer of an access-control policy. Verify suspicious traffic before blocking an address, because shared networks and dynamically assigned IPs can cause legitimate users to be affected. If you operate a site with a proxy or CDN, confirm which client IP Apache evaluates.
Before deploying changes, save the current .htaccess file, apply the smallest required modification, and test both blocked and permitted requests. If a configuration causes HTTP 403 responses for legitimate visitors or a server error, restore the backup and inspect the Apache error log. Hosting environments vary, so consult the server administrator when you cannot verify the applicable authorization behavior.
Authoritative Documentation
- Apache HTTP Server 2.4: Access Control — official guidance on authorization and IP-based access restrictions.
- Apache HTTP Server 2.4: .htaccess Files — official explanation of per-directory configuration and override behavior.
Author: Daniel Brooks
Author Description: Software and Web Infrastructure Specialist focused on Apache configuration, website operations, and practical access-control implementation.
Technical Review: The examples and deployment guidance explain Apache 2.4 authorization concepts. They are illustrative and should be checked against the live generator's actual output, the installed Apache version, and the hosting environment before use.