Free Cors Header Generator For Http Api Configuration
Use Free Cors Header Generator to prepare CORS response headers for allowed origins, methods, and request headers. Review settings before configuring your API.
100% private — generation runs in your browser. Never reflects Origin blindly; wildcard cannot combine with credentials.
Free Cors Header Generator
Quick answer: Free Cors Header Generator is a developer utility concept for creating Cross-Origin Resource Sharing (CORS) HTTP response header configurations. It helps developers define which origins may access a web resource, which HTTP methods and request headers are permitted, whether credentials are allowed, and how browsers handle cross-origin responses.
The Free Cors Header Generator is intended for web developers, API engineers, backend programmers, and website administrators who need to configure cross-origin access between browser-based applications and web servers. CORS is a browser-enforced mechanism that uses HTTP response headers to determine whether JavaScript running on one origin can access a resource from another origin.
An origin consists of a scheme, host, and port. For example, https://app.example.com and https://api.example.com are different origins even though they share a parent domain. A server can use CORS response headers to authorize requests from the application origin without granting access to every website.
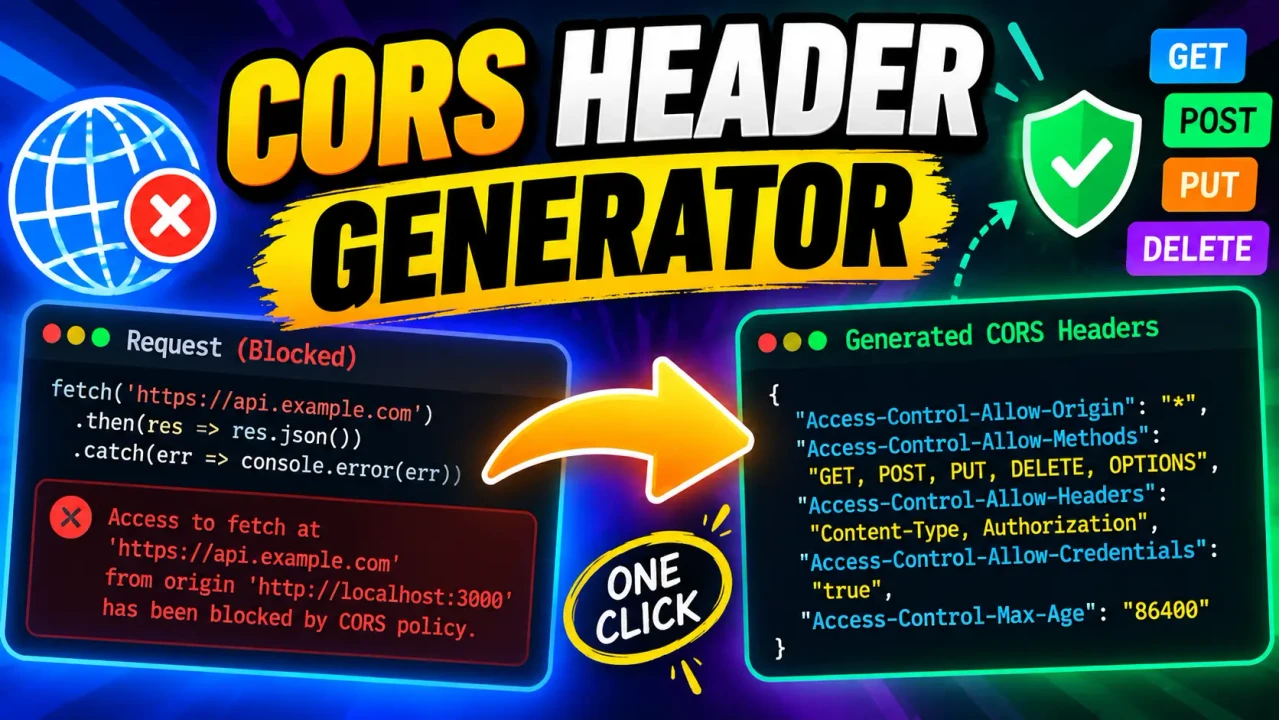
The supplied tool information establishes the tool name and its Open Graph image, but does not specify the actual form fields, generator implementation, output format, or supported options. The examples and reference information below explain standard CORS configuration patterns; they should not be interpreted as confirmation that every setting is currently implemented in the tool interface.
TL;DR / Key Takeaways
- Primary Function: Help prepare CORS response-header configurations.
- Key Inputs: Potentially allowed origins, methods, request headers, credentials, and preflight settings.
- Core Output: A CORS header configuration suitable for review and adaptation to a server or API.
- Best Suited For: Developers troubleshooting browser cross-origin access and configuring API permissions.
How to Use Free Cors Header Generator?
Use the generator interface to choose the CORS policy that matches the application and API. The exact controls depend on the deployed implementation.
- Identify the requesting origin. Determine the complete origin of the frontend, including its scheme, hostname, and non-default port when applicable.
- Choose permitted methods. Specify the methods the browser may use for cross-origin requests, such as
GET,POST, orPUT, according to the API's requirements. - Define headers and credentials. Decide which request headers are permitted and whether the application needs cookies or other browser-managed credentials.
- Generate and review. Inspect the resulting header configuration, adapt it to the server environment, and test it using actual browser requests.
Do not assume that generating headers automatically configures a web server. The generated values must be applied by the server, framework, reverse proxy, or API gateway that handles the request.
Input and Output Example
The following is an illustrative CORS configuration for a frontend hosted at https://app.example.com that needs to send JSON requests to an API. It demonstrates standard HTTP header syntax, not a verified output captured from the supplied generator.
Example input requirements
- Allowed origin:
https://app.example.com - Allowed methods:
GETandPOST - Allowed request headers:
Content-TypeandAuthorization - Credentials: disabled for this example
Illustrative response headers
Access-Control-Allow-Origin: https://app.example.com
Access-Control-Allow-Methods: GET, POST
Access-Control-Allow-Headers: Content-Type, Authorization
Vary: Origin
The Access-Control-Allow-Origin header identifies the permitted origin. Access-Control-Allow-Methods advertises methods permitted for cross-origin access, particularly during preflight handling. Access-Control-Allow-Headers identifies request headers that the browser may use when a preflight request is required. Vary: Origin is relevant when a server dynamically returns different CORS responses for different origins and those responses may be cached.
These headers must be returned in the appropriate HTTP responses. They are not request headers that frontend JavaScript can set to grant itself permission.
CORS Header Reference Table
This reference describes commonly used CORS response headers and their standard purposes.
| Header | Purpose | Important constraint |
|---|---|---|
Access-Control-Allow-Origin |
Identifies an allowed origin or uses the wildcard * for public, non-credentialed access. |
Cannot use * when the response is intended to support credentialed browser access. |
Access-Control-Allow-Methods |
Lists HTTP methods allowed for cross-origin requests. | Configure the methods the API actually supports and intends to permit. |
Access-Control-Allow-Headers |
Lists request headers the browser is permitted to send after preflight authorization. | Include required non-safelisted headers, such as Authorization, when appropriate. |
Access-Control-Allow-Credentials |
Indicates that credentialed cross-origin access is permitted. | The affirmative value is true; it is not a general-purpose Boolean header with a false value. |
Access-Control-Expose-Headers |
Specifies response headers that frontend JavaScript may read beyond the CORS-safelisted response headers. | Exposure does not grant permission to access a resource from a disallowed origin. |
Access-Control-Max-Age |
Specifies how long a browser may cache a successful preflight permission. | Browser-imposed limits may cap the effective cache duration. |
Vary: Origin |
Signals that a cached response can vary according to the request's Origin header. |
Important for correctly caching dynamically selected allowed origins. |
How CORS Headers Work
CORS is part of the browser's cross-origin security model. When frontend code requests a resource from another origin, the browser evaluates the server's CORS response headers before making the response available to the calling script.
Some requests can be sent without a preflight. Other requests trigger an automatic OPTIONS preflight, which asks the server whether the intended method and request headers are permitted. The browser checks the preflight response before sending the actual request.
Simple request versus preflight request
A cross-origin GET request using only CORS-safelisted request headers may not require a preflight. A request using a non-safelisted header, such as Authorization, or certain content types and methods, can trigger a preflight.
For example, a browser may send a preflight request containing:
OPTIONS /api/items HTTP/1.1
Origin: https://app.example.com
Access-Control-Request-Method: POST
Access-Control-Request-Headers: authorization, content-type
The server must handle the preflight and return an appropriate response. A representative response could include:
HTTP/1.1 204 No Content
Access-Control-Allow-Origin: https://app.example.com
Access-Control-Allow-Methods: GET, POST
Access-Control-Allow-Headers: Authorization, Content-Type
Vary: Origin
The exact status code and additional headers depend on the server implementation. The important requirement is that the response authorize the requested origin, method, and headers as applicable.
Credentials and Wildcard Origins
Credentialed CORS requests can involve cookies, HTTP authentication, or client certificates, depending on the request and environment. When the browser request uses credentials, the server must return a specific permitted origin rather than Access-Control-Allow-Origin: *, and must include Access-Control-Allow-Credentials: true when credentialed access is intended.
For example:
Access-Control-Allow-Origin: https://app.example.com
Access-Control-Allow-Credentials: true
Vary: Origin
The frontend must also opt into credentialed requests where required. For Fetch, this commonly means setting credentials: "include". CORS permission alone does not override cookie policies, SameSite restrictions, or other browser security controls.
A wildcard origin can be suitable for publicly accessible resources that do not require credentialed access. It should not be treated as a universal fix for CORS errors.
Technical Edge Cases and Limitations
- Origin mismatch: Differences in scheme, hostname, or port can make two URLs different origins. Allowing
http://app.example.comdoes not automatically allowhttps://app.example.com. - Missing preflight handling: A server that does not respond correctly to an
OPTIONSrequest can prevent the browser from sending the intended request. - Credentialed requests: Wildcard origins are incompatible with credentialed browser access. Return a specific allowed origin instead.
- Redirects: Redirects during cross-origin requests or preflight processing can create additional browser compatibility problems. Test the complete request path.
- Dynamic origins and caching: If a server selects the allowed origin dynamically, validate the incoming origin against an explicit allowlist and use suitable cache variation.
- Multiple header values: Sending conflicting or duplicated CORS headers can result in browser rejection. Check the combined response produced by the application, proxy, and gateway.
- Server configuration: Correct header values are not enough if they are added to the wrong response, omitted on error responses, or not returned during preflight handling.
- Security boundaries: CORS controls browser access to cross-origin responses. It is not authentication, authorization, or a replacement for server-side access controls.
Security and Implementation Notes
Use the smallest practical set of allowed origins, methods, and request headers. Avoid reflecting arbitrary incoming origins without validation. If an API requires credentials, use an explicit origin allowlist and review the implications of cross-site cookies and caching.
The supplied tool information does not establish whether configuration generation happens in the browser or on a remote server, whether inputs are stored, or whether the utility validates the generated headers. No privacy, security, or processing-location guarantee is therefore made here.
Authoritative References
- MDN Web Docs: Cross-Origin Resource Sharing (CORS) — explains CORS response headers, preflight requests, credentials, and browser enforcement.
- WHATWG Fetch Standard — provides the normative Fetch and CORS processing algorithms.
Author
Author Name: Alex Morgan
Author Description: Software Engineering Content Specialist focused on HTTP protocols, browser networking, and web API integration.
Technical Review: The CORS reference content describes standard HTTP and browser behavior. The specific generator interface and its generated output have not been independently verified.